How to Check Your Browser and Server Certificate Security After the eMudhra Incident

The October 2026 eMudhra certificate incident has encouraged website administrators and internet users to pay closer attention to HTTPS certificate security.
Mozilla confirmed the compromise of private keys associated with eight intermediate certificate authorities and implemented protections in Firefox.
While most users do not need to manually inspect every certificate they encounter, keeping software updated and understanding certificate warnings remain important.
Start by Updating Your Browser
Browser developers maintain certificate trust information and security mechanisms.
Use the browser’s official update process to ensure you receive relevant security changes.
Firefox users should review Mozilla’s published guidance concerning the eMudhra incident, especially if they use unusual configurations or enterprise-managed environments.
Check Operating System Updates
Some applications rely on operating system certificate stores rather than a browser-specific trust store.
Keeping the operating system updated helps ensure that relevant security changes reach supported components.
Understand Certificate Warnings
Browsers may warn when a certificate has expired, is not trusted, does not match the requested domain, or fails another validation check.
Do not bypass unexpected certificate warnings on sensitive websites, especially banking, email, administration, and payment pages.
Instead, verify the address and contact the website operator if the problem persists.
Inspect a Website Certificate
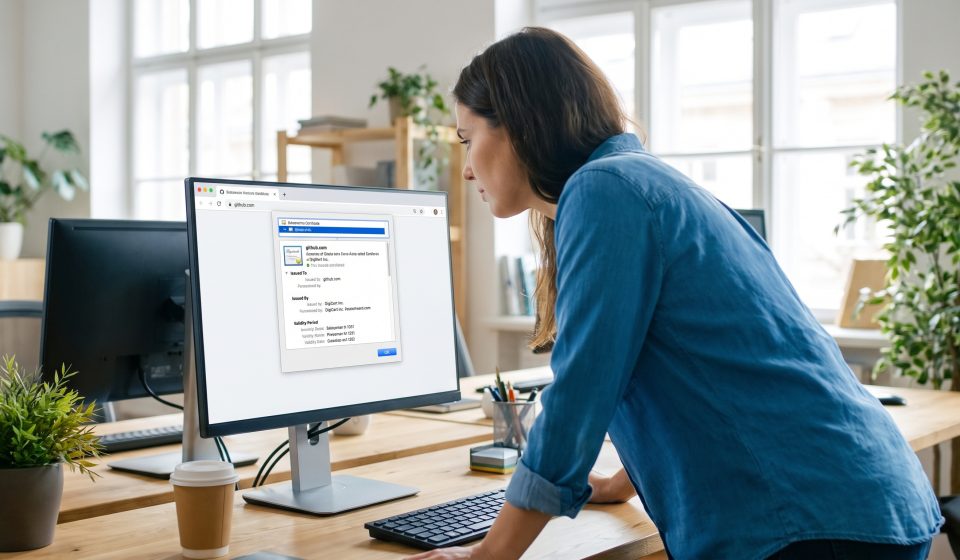
Modern browsers generally provide a way to view connection security information and certificate details, although the exact interface varies by version.
Administrators can inspect the issuer, subject, validity period, and certificate chain.
Remember that a certificate’s issuer name alone is not enough to establish whether a specific compromised key is involved.
Check Your Server’s Certificate Chain
Website operators should identify which certificate and intermediate authorities their server presents.
Compare those details with the affected certificates described in authoritative incident reports.
If your certificate provider or hosting company manages certificate deployment, ask whether customer action is necessary.
Do Not Replace Certificates Without Evidence
Unnecessary certificate replacement can cause outages if the new chain is installed incorrectly.
Follow your certificate provider’s instructions and confirm whether your actual certificate chain is affected.
Review Other Applications
Browsers are not the only software using TLS.
Email clients, APIs, enterprise applications, and other network services may rely on different trust stores or update mechanisms.
Organizations should inventory important services and verify that security updates have been applied where necessary.
Maintain Certificate Hygiene
Protect private keys, automate renewal where appropriate, monitor expiration dates, and document certificate ownership.
Regular reviews can reduce avoidable outages and simplify incident response.
Additional Reading
Read our eMudhra certificate compromise report and TLS certificate fundamentals guide.
Frequently Asked Questions
Do I need to replace my SSL certificate because of eMudhra?
Not automatically. Check whether your certificate chain is affected and follow official provider guidance.
Should I ignore browser certificate errors?
No. Unexpected certificate warnings can indicate security or configuration problems.
Will browser updates help?
Yes. Browser updates and trust-store protections are important responses to certificate incidents.
Can an outdated application have different certificate risks?
Yes. Applications may use different trust stores and may not receive the same protections at the same time.
Does HTTPS prevent server vulnerabilities?
No. HTTPS protects communication in transit but does not eliminate application or runtime vulnerabilities.